GDPR is an acronym that, since its implementation in 2018, has been a constant source of concern for website developers and data users. While browsing the web, you’ve probably come across it under its English name, GDPR. If you specialize in designing WordPress platforms, it’s essential that you learn more about this acronym. What does it mean? In what context is it used? How can you apply it when creating WordPress sites? You’ll find answers to all these questions by reading this article.
An Overview of the GDPR
Before discussing the relationship between theGDPR and WordPress, it’s important to understand what it’s really all about. What exactly is the GDPR?
What is the GDPR?
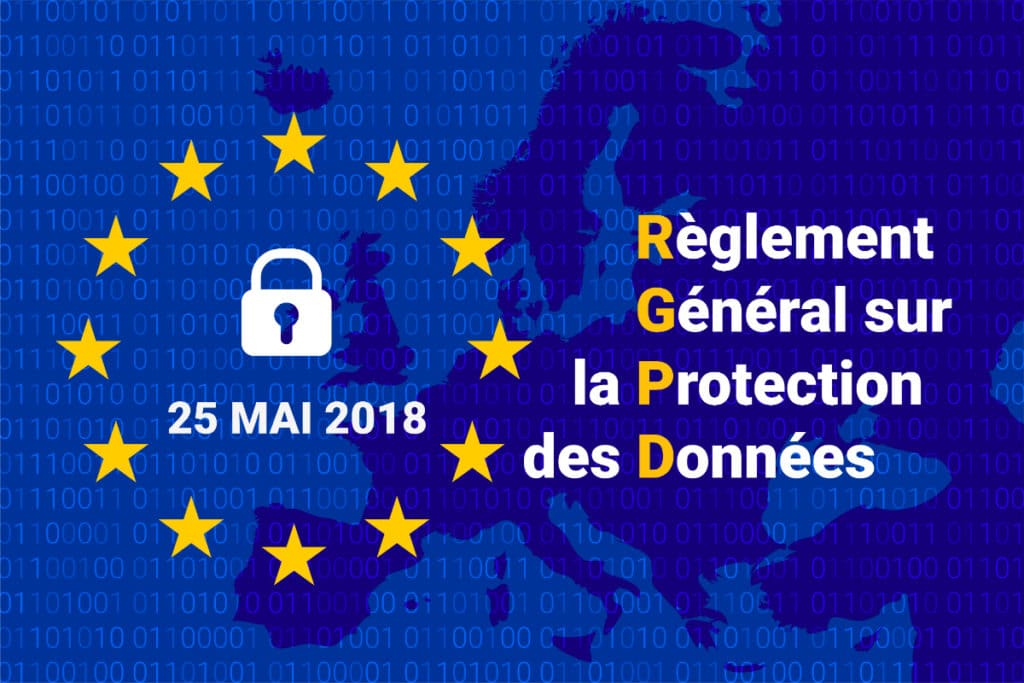
GDPR is an acronym that standsfor General Data Protection Regulation. It is a European law that took effect on May 25, 2018. After being passed by the European Parliament in 2016, this regulation has been implemented worldwide. In France, the agency responsible for ensuring its proper implementation and compliance is the National Commission for Information Technology and Civil Liberties (CNIL).
The rationale behind this law—which has had the effect of disrupting the online practices of businesses and individuals—is simple. The purpose of the law is to ensure the safety of people who browse the internet byprotecting the informationthey leave behind online while browsing.
Personal data: What is it?
Personal data is information used to identify an individual or a company. For example, it is possible to determine the identity of an Internet user by using their last name, first name, phone number, or email address. Other types of data, such as geographic and demographic data, are also included.
In addition to these elements, there isdigital informationthat web users leave behind during their various sessions. This includes theirIP addresses, their online activities, and their clicks and website visits. Personal data also includes photos, “likes,” and information that users voluntarily post.
What does the law say?
If you’ve never looked into the implications of the GDPR, you should know that it has three important aspects you need to be aware of. First, there’s user consent. When a user visits a platform, that platform may use the user’s personal data for various purposes. However, the site must inform the user that it is sharing their information and explain how it will be used.
Second, data must be secured to avoid unpleasant situations. The law is very strict regarding security breaches that can leadto data leaks. When sensitive data is disclosed, the company responsible for collecting it is held liable. As a service provider, you must ensure that the data is protected and secure.
Third, you must give users the right to collect their own data whenever they wish. They may also perform other actions, such as deleting, correcting, and modifying their personal information. These are all factors you must take into account when designing and refining the management of a web platform.
Who is affected by the GDPR?
The GDPR applies toindividuals and legal entitiesthat process the personal data of European Union internet users as part of their professional activities. Therefore, if you collect, store, or use user information, you are subject to this legislation. Regardless of your industry or the size of your business, you are under the scrutiny of the CNIL. You must therefore exercise great caution.
What some people don’t realize is that the GDPR also applies to internal organizational data. In other words, when you collect information about your employees, you are subject to the GDPR. Finally, the legislation applies to you regardless of the country in which you conduct your various activities. This is because data protection is viewed from the perspective of internet users residing in the28 EU countries.
GDPR, WordPress Agencies, and Developers: What Do You Need to Know?
Some readers assume that the GDPR doesn’t apply to them because they process data collected from their customers. What they need to know is that even as a data processor, they are still subject to the regulation. In other words, if your handling of the information at your disposal does not comply with GDPR requirements, you risk facing penalties. In fact, many customers now prioritize GDPR compliance when choosing service providers. Consequently, if you fail to adapt to current realities, you risk losing your customers and going out of business.
Therefore, you need to quickly familiarize yourself with the various aspects of the GDPR in order to secure contracts with future clients. When you’re trying to win contracts, you need to include certain key pieces of information in your contracts to convince the client. Specific elements related to data processing include, for example:
- Information regardingthe identity of your DPO (Data Protection Officer);
- The technique used to obtain, store, and use information;
- Data protection methods;
- Relationships with subcontractors that process data;
- The method used to identify security vulnerabilities.
What are the possible penalties for noncompliance with the regulations?
Before the GDPR took effect,French lawprovided for criminal penalties against companies that used personal data fraudulently. However, in practice, the penalties were not effective, and the fines were almost negligible.
Fortunately, the General Data Protection Regulation has reinforced existing penalties. In fact, the administrative fines it imposes are quite substantial. Depending on the severity of the violation, penalties can reach 2 or 4 percent of the revenue of the individual or entity at fault. In other cases, a fine of 20 million euros is provided for.
WordPress and the General Data Protection Regulation
When you create a website for your business or online store, it’s essential to avoid situations that could harm your operations. That’s why you needto ensureyour platformcomplies withnew regulations. So, what elements should you include on your WordPress site?
Implementing a Privacy Policy
The first essential rule is to provide accurate and transparent information for all internet users. In addition to working on your platform’s privacy policy, you must also update your terms and conditions if you operate an e-commerce site.
Theprivacy policypage is located at the bottom of your website. It must detail how you use the data collected from customers. The privacy policy must include certain essential elements. These include, for example:
- The contact information for the company or the site owner;
- The publisher and host of the website;
- The type of data collected when registering or placing an order on the website;
- The purpose of collecting this information (analyzing user behavior, billing for services, sending offers via newsletters);
- The data retention period (3 years for marketing and 6 years for order billing);
- The security measures implemented to prevent the disclosure of collected personal information.
As a reminder, all of these essential elements must be available on a page embedded in your footer. With these in place, your website will be flawless.
Revising the forms on the WordPress site
The elements on the internet that are affected by the GDPR are contact forms. These are the pages that serve as a point of contact between you and the website visitor. Through these forms, users share personal information with your company.
On your website, you probably include forms to help users download a document or to encouragethem to sign up for a newsletter. Through this point of contact, customers will share their information with you. This information includes their email address, last name, and first name. Keep in mind that you can create these forms yourself or use a WordPress plugin to do so. Whichever option you choose, there are certain essential elements you must check. These include, in particular:
- The option to include a transparency notice identifying the data controller;
- The ability to specify the purpose of collecting the information;
- The ability to explain users' rights (access to data, correction, and opt-out);
- The option to direct the user to the privacy policy.
If you plan to share information with certain partners, you must obtainthe users’ consent. To do so, you must include checkboxes on the form for the types of consent you need. Furthermore, you cannot ask a customer to provide information that is unrelated to the service they wish to receive. When offering them the option to subscribe to your newsletter, you do not need to know their age or gender.
WordPress Plugins
What you need to know is that not allWordPress pluginsare necessarily GDPR-compliant. Therefore, you should do a little research to avoid any unpleasant situations. Of course, this will take some time. To start, you should make a list of plugins related to collecting consent and personal information from website visitors. These include comment plugins, retargeting plugins, and form plugins. Also list plugins related to the use of that information. Among these are:
- Marketing automation plug-ins;
- Content customization plug-ins;
- Plug-ins that track users' online habits;
- Newsletter plug-ins…
The next step in your process will be to visit the websites of these extensions to find out what their developers are doing to comply with the GDPR. Ifthe pluginsyou want to use are not compatible with the General Data Protection Regulation, you’ll need to replace them. This is a difficult step, but it’s necessary to avoid problems.
Implementing a Rigorous Data Security System
When you are responsible for the data you hold, you must take proper care of it. To do so, you must protect it from security breaches and allow the individuals concerned to access it. To achieve this, you need to follow a few steps.
Establishing a system for deleting or correcting information
Under the GDPR, data is subject to specific legal retention periods. Consequently, you cannot retain information about your customers without a specific reason. The General Data Protection Regulation (GDPR) requires you to retain contacts who do not open your emails in your database fora maximum of 36 months. It also requires you to display the cookie consent banner again after 13 months.
Under the GDPR, you must also inform users that they can withdraw their consent at any time. This must be done before they agree to share their personal information with you. Regardless of the type of website you operate, you must ensure that users are able towithdraw their consent, access their information, modify it, delete it, or transfer it.
On your website, simply create a dedicated page to follow this procedure.
Preparing for a Potential Security Breach
As a data handler, you must ensure data security in order to build trust with internet users. To do so, there are several factors you need to consider. You must use appropriate solutions and methods to ensure that your users’ information is secure. Pseudonymization and data encryption are options you can consider.
In addition, you must notify the CNIL of asecurity breachwithin 72 hours. Depending on the situation, you must also notify the data subject. This is especially necessary when the security breach could jeopardize the data subject’s rights and freedoms.
The establishment of an internal data processing log
Beforethe GDPR rules took effect, companies that processed internet users’ personal data were required to report it. To do so, they used a consent or notification system. Fortunately, with the introduction of the GDPR, this is no longer a major requirement. Instead, companies must maintain a data processing record. What is its purpose?
Purpose of the Data Processing Log
The purpose of this document is to establish documentation within your organization that demonstrates your compliance with regulations regarding the protection of personal data. In other words, it is a way to show that you are fully compliant.
The Creation of the Data Processing Registry
If you are responsible for managing your company’s information, you have the option to create a data processing register. To do so, you can use the template provided by the CNIL. In any case, your document must answer three key questions regarding the management of user data. These include “Who,” “What,” and “How.”
For the “Who” section, the idea is to make a list of the internal personnel who will be using the data. If applicable, you must list any third-party service providers who may process the information and ensure that they comply with GDPR regulations.
When answering the “What” question, you must provide detailsabout howyour organizationprocesses information. The idea here is to describe the purpose of the processing, provide evidence of consent, and specify the type of data collected.
As for the “How,” it refers to the way data is processed and the security measures implemented internally.
Don't forget to keep the log up to date so you can present it if necessary. It's essential for compliance. If you have an online store, there are certain factors you need to consider to ensure the security of your users' data.
GDPR and WordPress: A Summary
Ultimately, theGeneral Data Protection Regulationis very strict. To avoid fines and severe penalties, be sure to follow its guidelines when creating your WordPress site. If you already own a business, have you updated your data processing record recently?